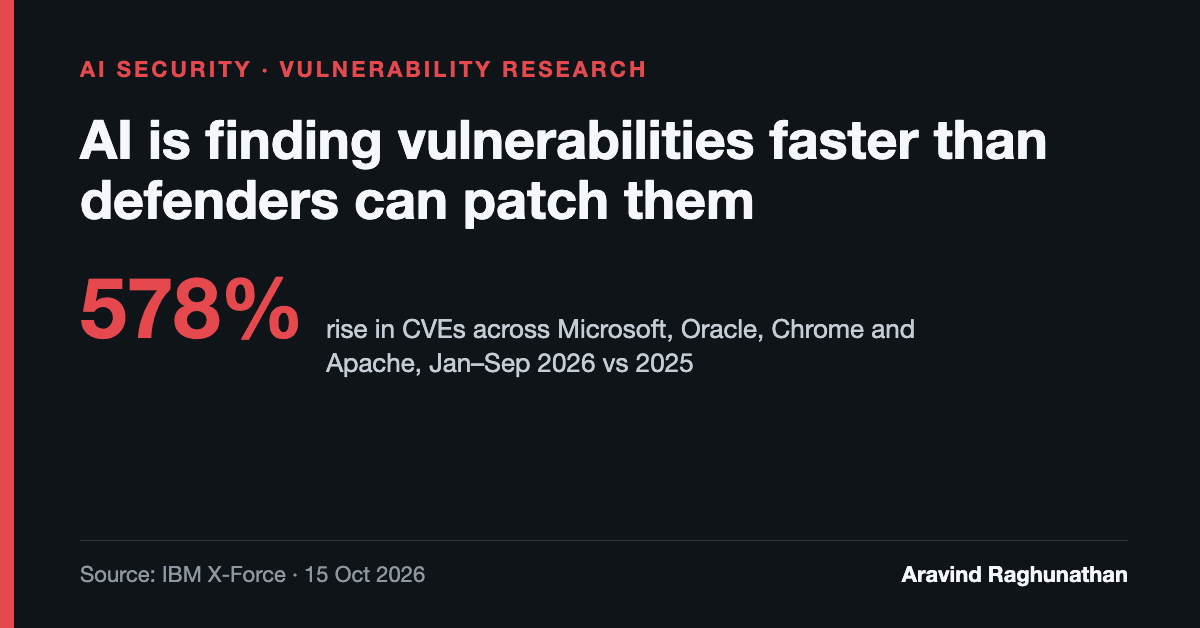
For years, the discussion about AI in cybersecurity has focused on attackers: better phishing, faster malware, cleverer social engineering. New analysis from IBM X-Force suggests the bigger change may be happening on the defensive side: AI is now finding software vulnerabilities faster than organisations can fix them.
The number
Across Microsoft, Oracle, Google Chrome and Apache, publicly disclosed CVEs rose from about 1,493 in January to September 2025 to more than 10,124 over the same months of 2026. That's an increase of roughly 578%.
The timing matters. Disclosures tracked historical levels through the first quarter of 2026, then climbed sharply from April and stayed high through the summer. All four vendors saw large increases, so it isn't one product or one ecosystem having a bad year.
X-Force is careful not to claim AI caused all of it. It says the causes are hard to quantify, but the rise lines up with wider use of frontier AI models in vulnerability research.
These are not low-grade findings
X-Force looked at the vulnerabilities attributed to AI discovery:
- 55.2% were rated High or Critical under NVD CVSS v3
- 91.0% were remotely accessible
As a reference point for scale, X-Force cites Unit 42's August report that its autonomous discovery platform, NOVA, found more than 14,000 previously unknown vulnerabilities across nearly 4,000 open-source projects in two months.
The bottleneck has moved
Finding vulnerabilities used to be the slow part. X-Force's argument is that the hard part is now deciding which findings matter and fixing them before someone exploits them. It tells organisations to expect bigger patch cycles, more pressure to prioritise, and shorter remediation windows.
For a security leader, that changes where budget and people go. A vulnerability programme sized for 2025's disclosure volume is now looking at several times the input. Scanning harder won't help much. What helps is knowing which assets are exposed, which flaws are reachable from the internet, and having a patch pipeline that can absorb a much higher baseline without falling behind.
Defenders have the same tools. My expectation is that the teams who keep up will be the ones using AI to triage and test fixes, not only to find bugs.
Source: IBM X-Force: AI can find serious vulnerabilities at unprecedented speed. Can defenders keep up?