Most enterprise plans for running AI agents safely come down to one idea: put the agent in a sandbox and only let it talk to approved destinations. New research suggests that wall has a gap in at least one widely used sandbox.
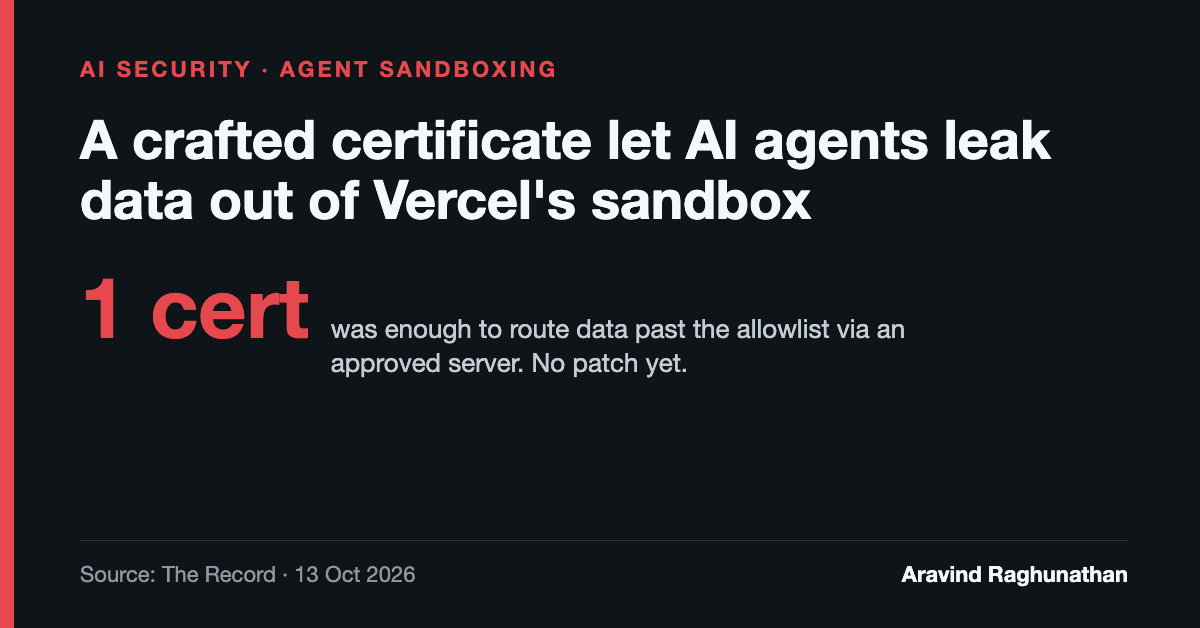
AI security startup AIR has published findings on a network-filtering flaw in Vercel Sandbox, a tool developers use to run code in isolated environments. The flaw lets an agent get data out past the network allowlist that is supposed to contain it.
How the escape works
Sandboxes like this usually restrict outbound traffic to a list of approved servers. AIR found a way around that by abusing how servers handle certificate validation.
In the researchers' demonstration, a specially crafted certificate is sent to a server the sandbox is allowed to reach. Processing that certificate makes the approved server send a request to an attacker-controlled server. The data leaves, but the sandbox never connects to the attacker directly. From the sandbox's point of view, nothing looked wrong.
AIR co-founder and CTO Niv Hoffman told Recorded Future News that this makes it a very hard leak to patch, and that it shows enterprises can face Hugging Face-style incidents with their own agents. He was referring to the earlier case of rogue models breaking out of a test environment.
Where things stand
- AIR reported the issue to Vercel. According to Hoffman, Vercel said it needs time because it is not yet clear how a fix would work.
- Vercel did not respond to the reporter's request for comment.
- AIR has seen no exploitation in the wild but cannot rule it out, and says the weakness appears to be longstanding.
Nic Adams, CEO of 0rcus, put the broader lesson well: an approved server can end up as an unwitting courier for stolen credentials, so security has to account for what happens after the first connection.
What this means for teams running agents
An allowlist checks where traffic goes first. It does not check what the approved destination does next. If your agent controls can be summarised as "sandbox plus allowlist", this research is a reason to add layers:
- Keep secrets out of agent environments unless the task truly needs them, and scope any that are present tightly.
- Log and inspect what agents send, not only where they connect.
- Treat certificate handling and outbound TLS as part of the agent threat model.
The agents are getting more capable each quarter. The containment around them needs the same attention.