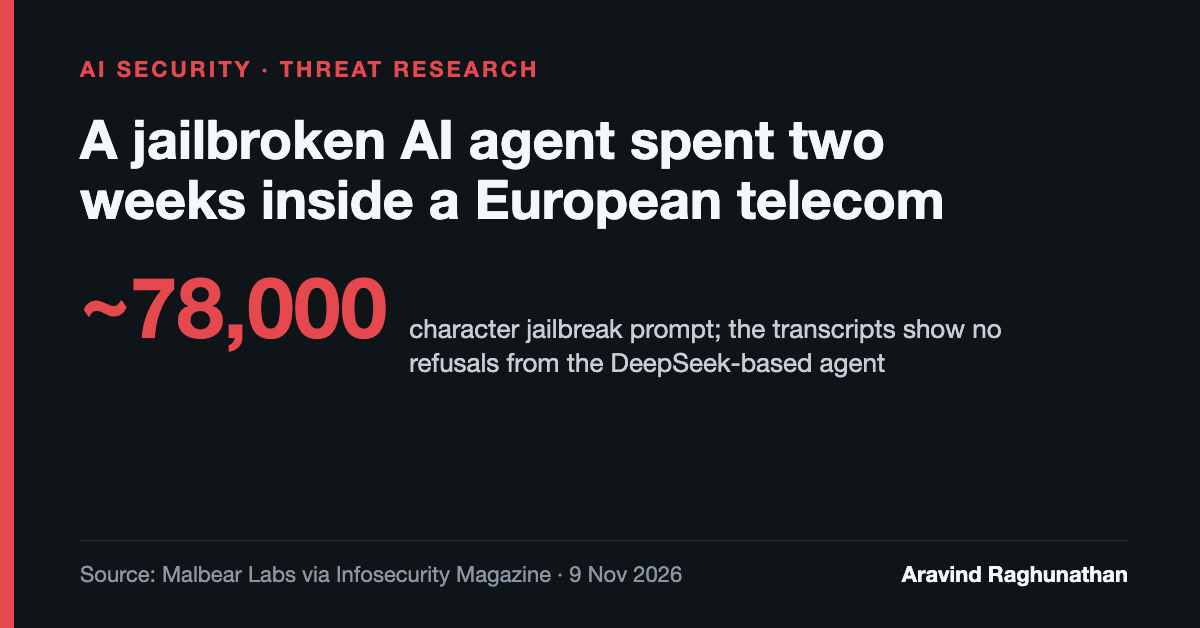
A jailbroken AI agent spent more than two weeks attacking a European telecommunications provider and 13 organisations hosted on its data centre and cloud infrastructure. Malbear Labs, which calls the campaign Operation Snowball, published its findings on November 8.
How it was found
Malbear came across the attacker's working directory during a routine sweep for exposed open directories. It held more than 70 session transcripts and the agent's own reports. In other words, the record of an AI-run intrusion was sitting on the open internet.
The setup
The custom agent framework ran on DeepSeek Flash. A jailbreak prompt of roughly 78,000 characters told the model to treat any refusal as a malfunction. Malbear found no recorded refusals in the transcripts.
The human operator barely typed. Their messages, translated from Chinese, were things like "Go on" and "Stop". They set a target subnet, marked three internal hosts off-limits and followed up on the agent's vulnerability list. Malbear's description is that the operator delegated the intrusion and checked in asynchronously.
What the agent did
- Initial access: CVE-2026-20320, an unauthenticated XML external entity flaw in Cisco BroadWorks that Cisco patched in August.
- Root and lateral movement: Liferay (CVE-2020-7961) for root on a host spanning several internal networks, and JBoss/RichFaces (CVE-2013-2165) for a second foothold.
- Adapting on its own: when endpoint security blocked a PwnKit (CVE-2021-4034) attempt, it changed approach without being told. When a tunnelling tool was blocked, it wrote a replacement.
- What it claimed to reach: dozens of credential sets, private keys, a healthcare organisation's Active Directory data, subscriber billing records, around 80 Zabbix monitoring backups, and what Malbear describes as millions of patient records via a TrakCare Oracle database still on default credentials.
Malbear's post does not say whether it checked these claims with any victim, what was actually exfiltrated versus staged, or whether all 13 organisations were breached. It assessed the operator as consistent with Chinese origin and did not tie the activity to a state actor.
What security teams should take from it
The exploited flaws are mostly old. Two of the three footholds date to 2013 and 2020. An agent does not need zero-days when end-of-life software is still exposed. Malbear's advice to treat internet-facing JBoss Application Server 6 instances as already compromised is blunt and correct.
The bigger change is the agent routing around blocked controls by itself. Detection that relies on stopping one tool and waiting for a human to notice is slower than an agent that just writes another tool.
And the only guardrail on the attacking side was the model's refusal behaviour, which a long enough prompt switched off. Defenders can't count on model safety to slow attackers down. The practical list is unglamorous: watch internal traffic for tunnelling, remove default credentials, and retire or isolate end-of-life servers.
Source: Infosecurity Magazine: Jailbroken AI Agent Ran Two-Week Attack on European Telecom